Track your test coverage
You have seven catalogues ready to load, from WSTG to NIST SP 800-115.
They include the 267 ASVS requirements.
Each checked item links to the finding that provides its evidence.

For pentesters
A test reveals an issue: what should the client receive?
Record the finding, steps and evidence, then prepare the report and its review.
After remediation, record the retest and its outcome. Automated analysis remains limited to supported scanners.
A 30-minute demo on a project close to yours.
From finding to deliverable
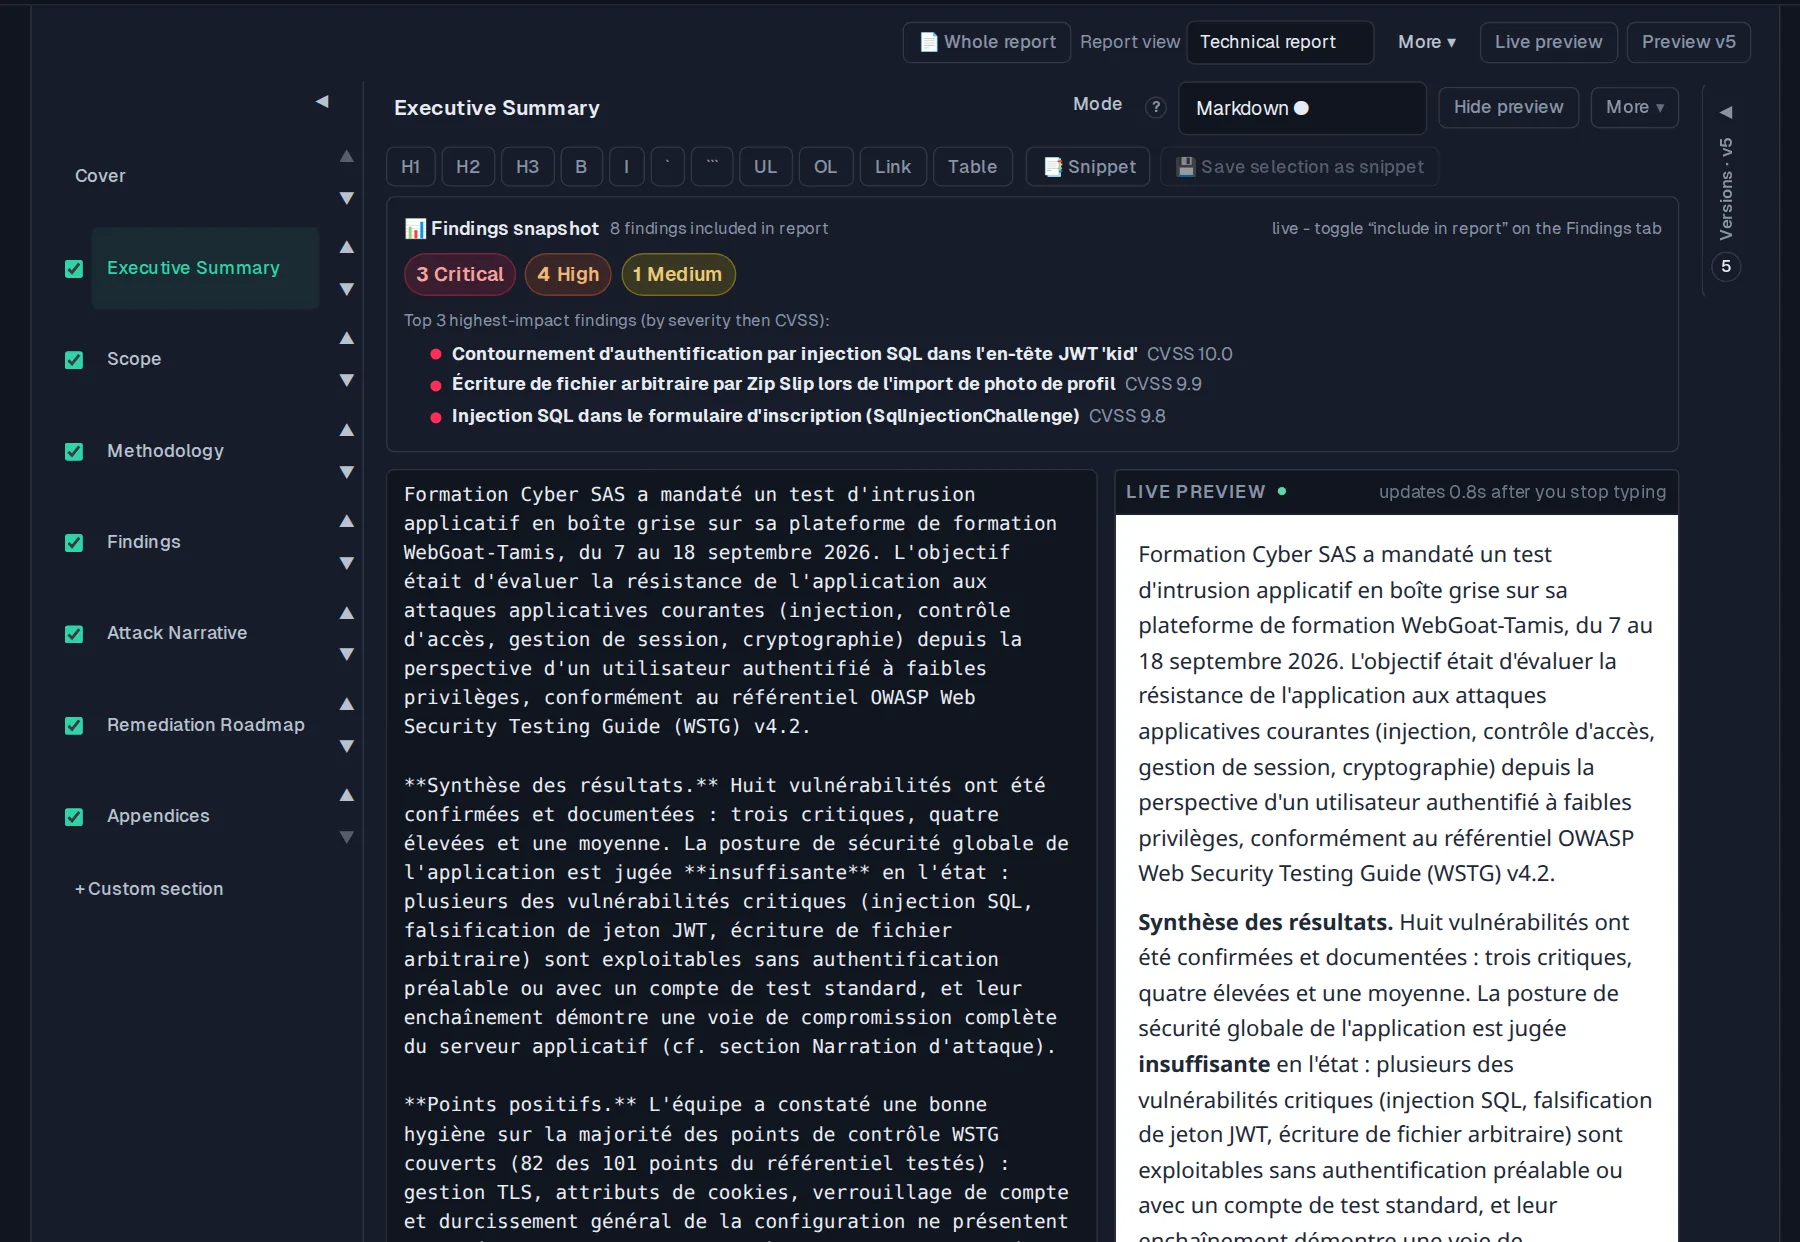
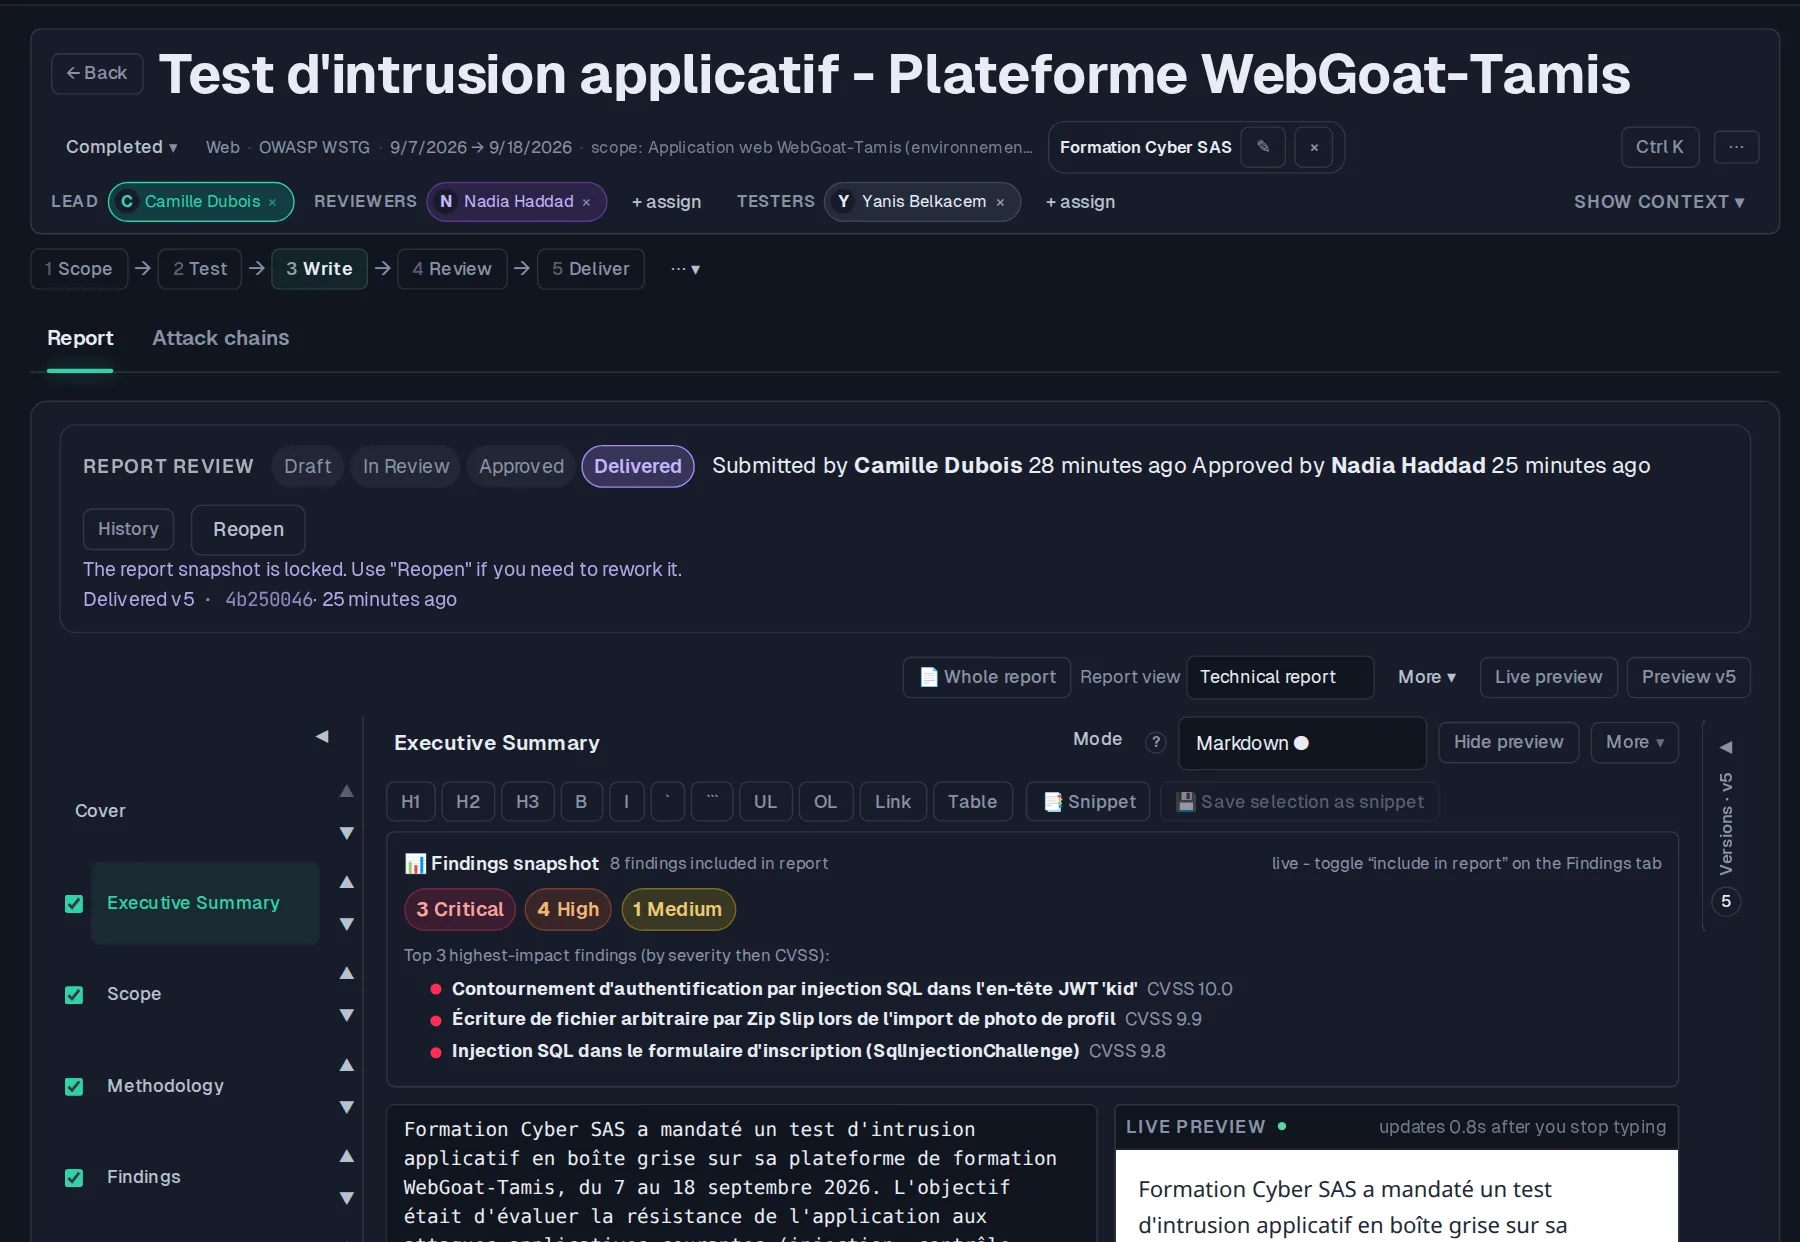
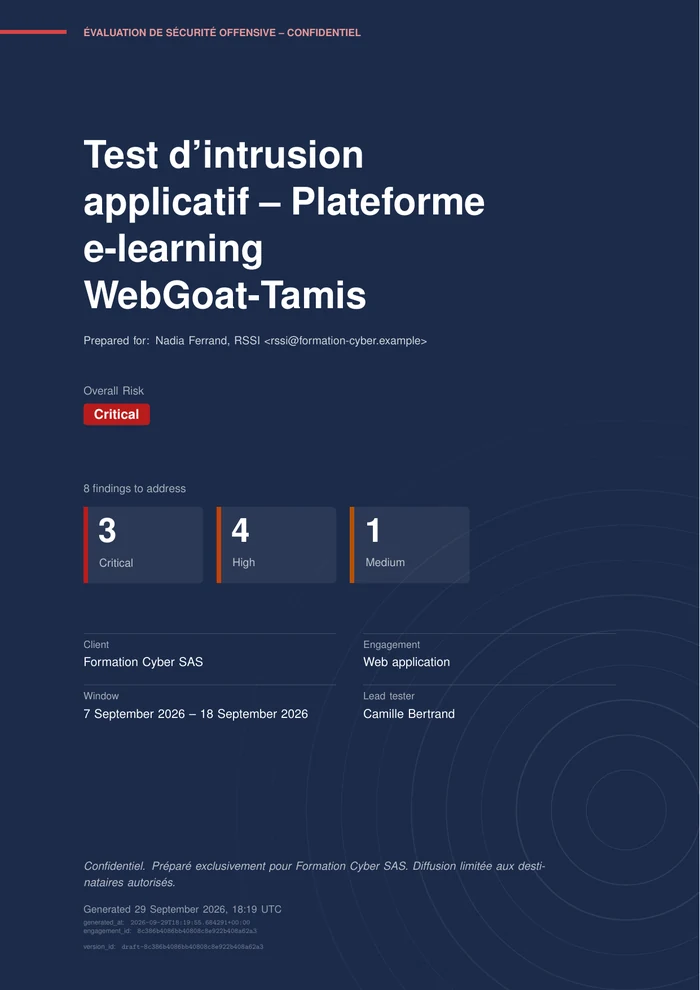
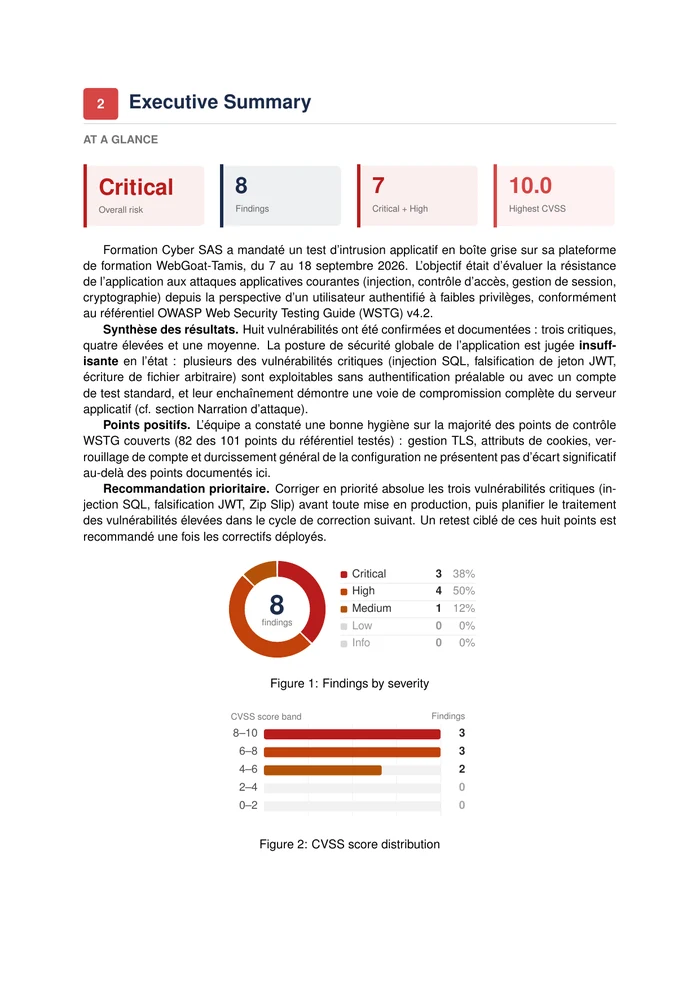
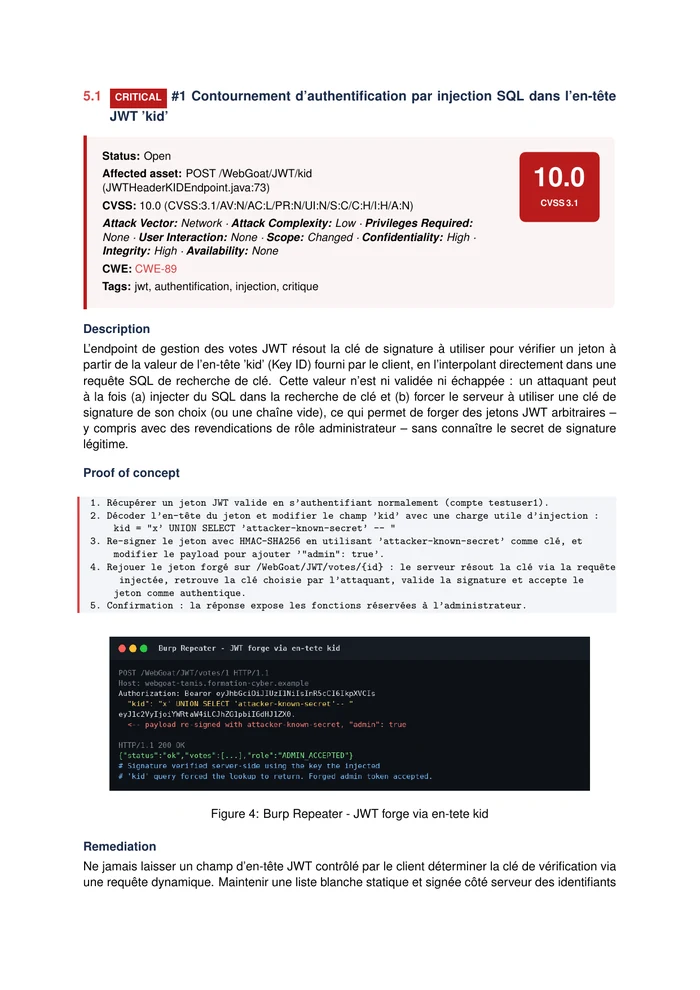
Four steps, one tool: a finding entered once feeds the report, the review and the delivered PDF.
Demo screenshots. Results illustrate this project, not every project.
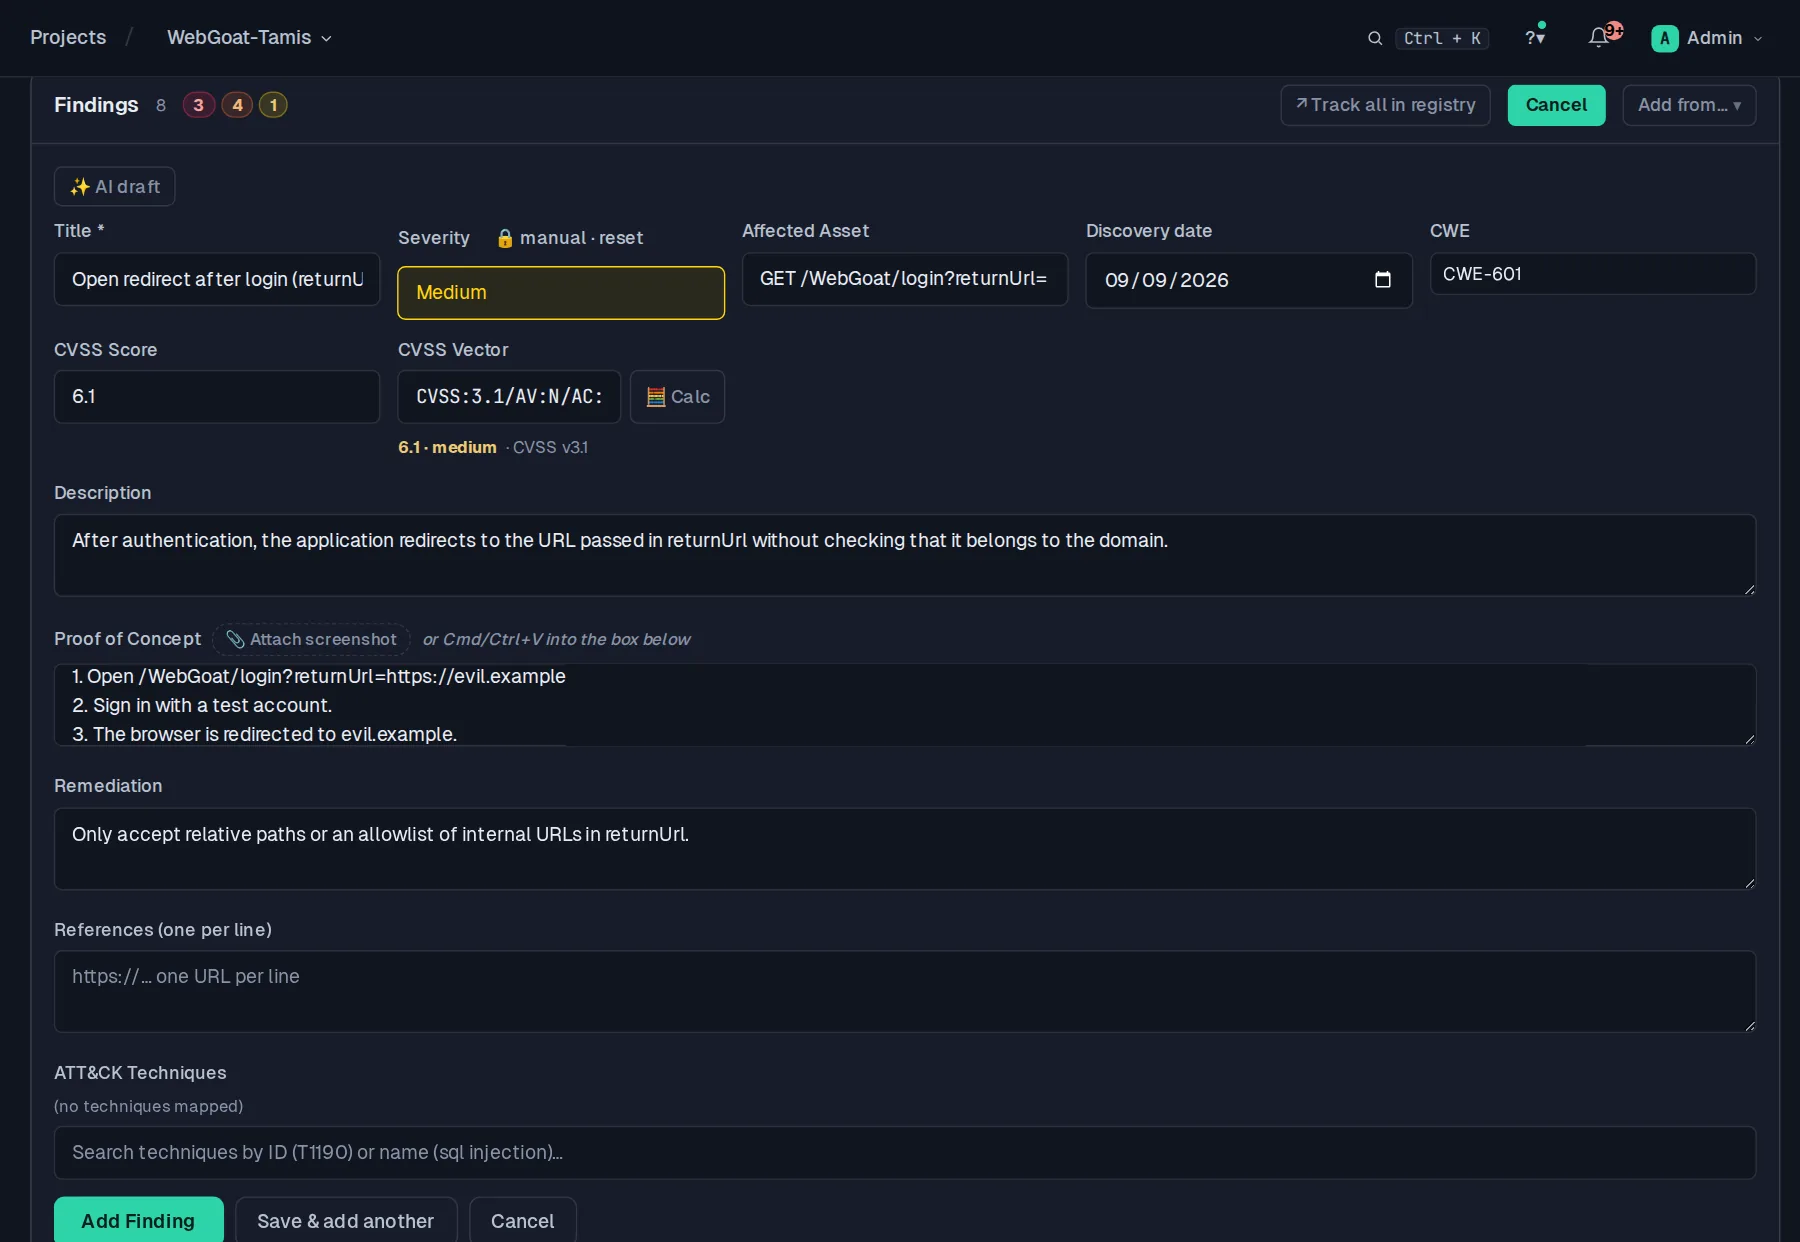
Tamis interface · scanned WebGoat project
Under the hood
In Tamis
You have seven catalogues ready to load, from WSTG to NIST SP 800-115.
They include the 267 ASVS requirements.
Each checked item links to the finding that provides its evidence.
Your findings connect into a scenario mapped to the MITRE ATT&CK techniques they cover.
That scenario stays linked to the threat in the architect's model.
For findings from supported scanners, you can rerun the scanner on the fixed asset.
Before delivery, the report must be approved by someone other than the person who submitted it.
You can also export drafts in the client's branding.
On the same evidence
Good to know Tamis gives you tools for the engagement.
Your expertise as a pentester remains essential.
DAST is limited to existing environments in the engagement scope, after ownership of their origin has been verified.
On the blog
The mechanics explained simply, then in depth. All articles