For CISOs and GRC teams

A risk to address.
A decision to document.

A project risk needs a decision.
Review the associated findings and evidence, then assign an owner, treatment and deadline.
Retain the decision rationale and the material to present at a review or audit.

Request a demo 

A 30-minute demo on a project close to yours.

With Tamis, step by step.

    From evidence to decision

    Steer risk, not alerts.

    Three screens: the decision queue, governance and EBIOS RM risk analysis.

    Demo screenshots. Results illustrate this project, not every project.

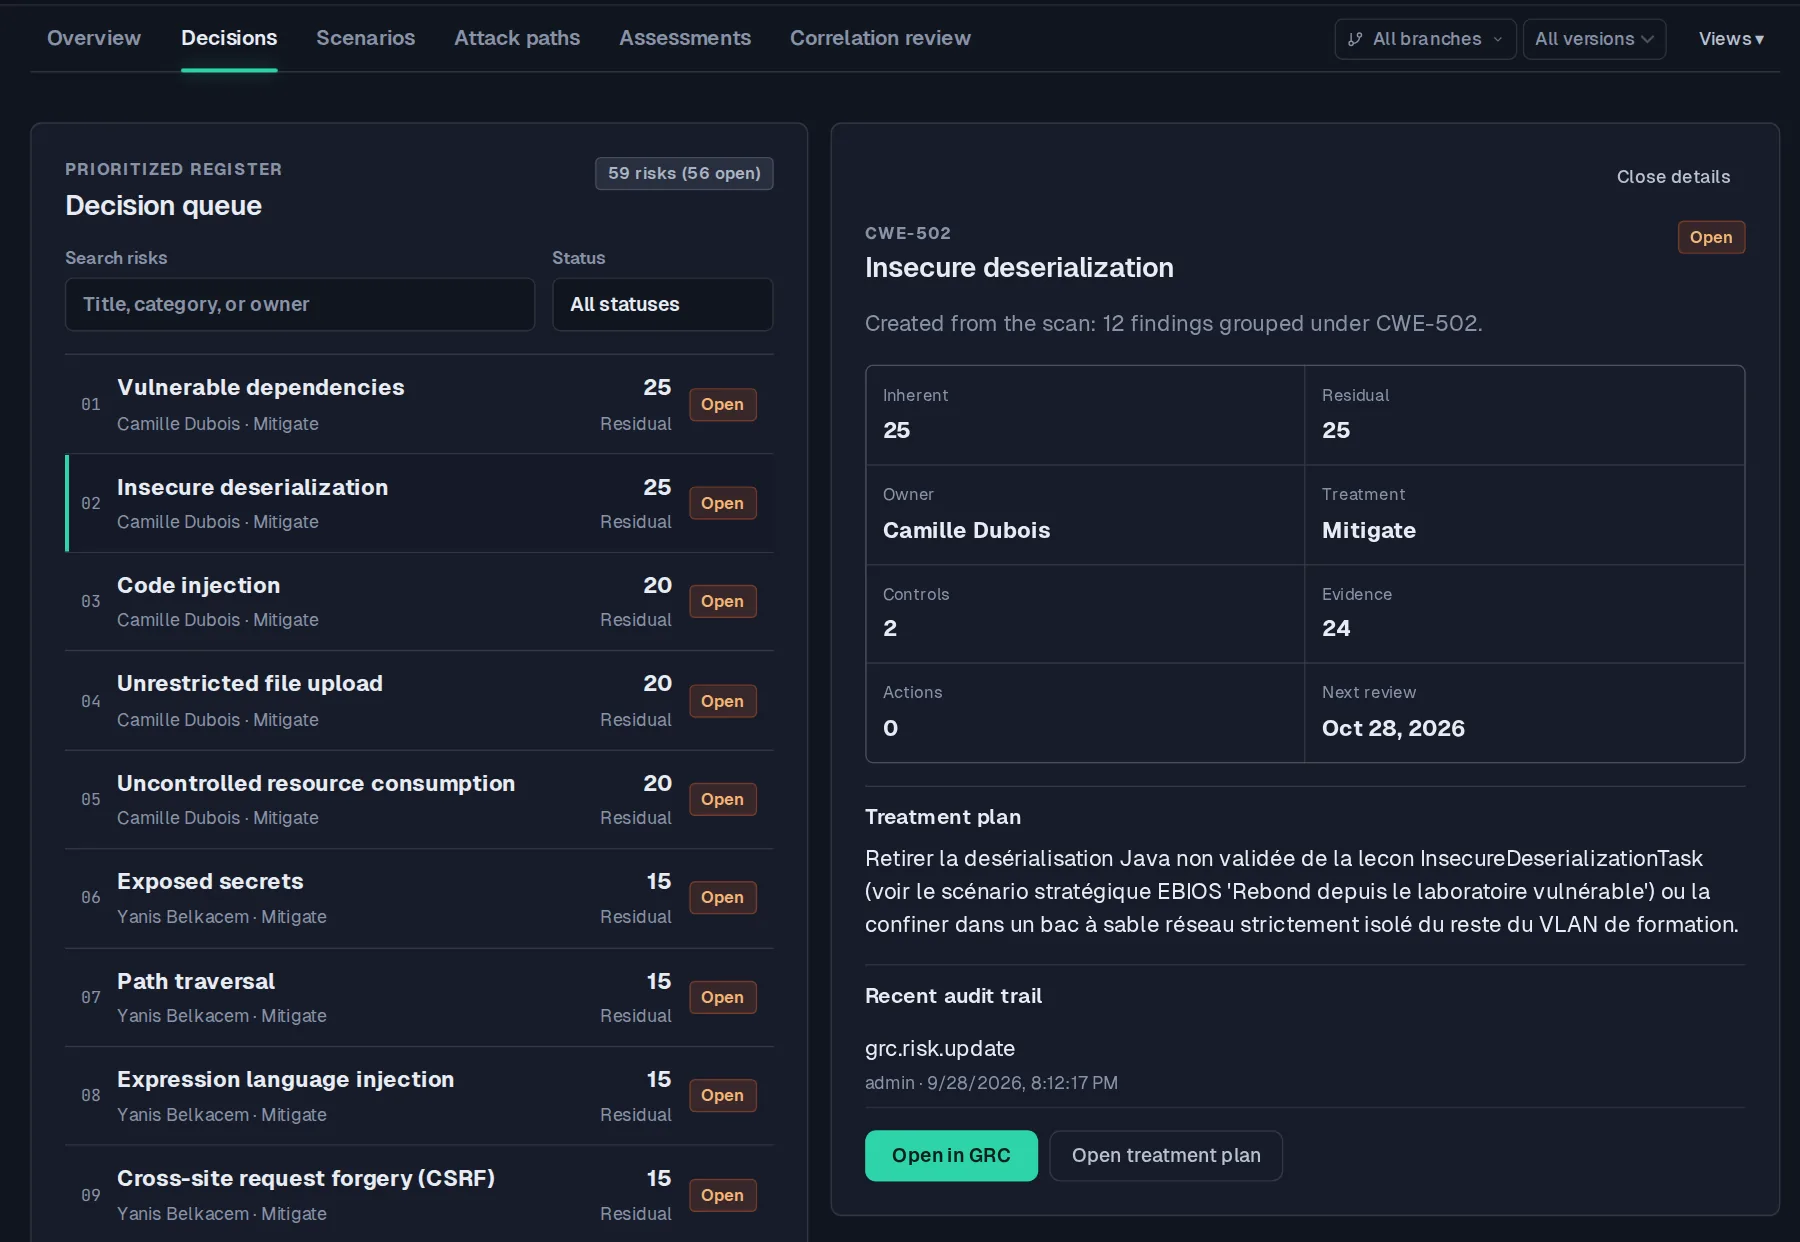
    Decision queue: risks ranked by residual score, with owner, treatment, controls and evidence
    A risk needs treatment. Inspect its evidence, assign an owner and document the decision in the review queue.

    Tamis interface · scanned WebGoat project

    Under the hood

    Frameworks
    Connect your findings to 224 CWE-linked controls across 16 frameworks.
    Cockpit
    Focus your review on at most twenty actions per project, each backed by evidence.
    EBIOS RM
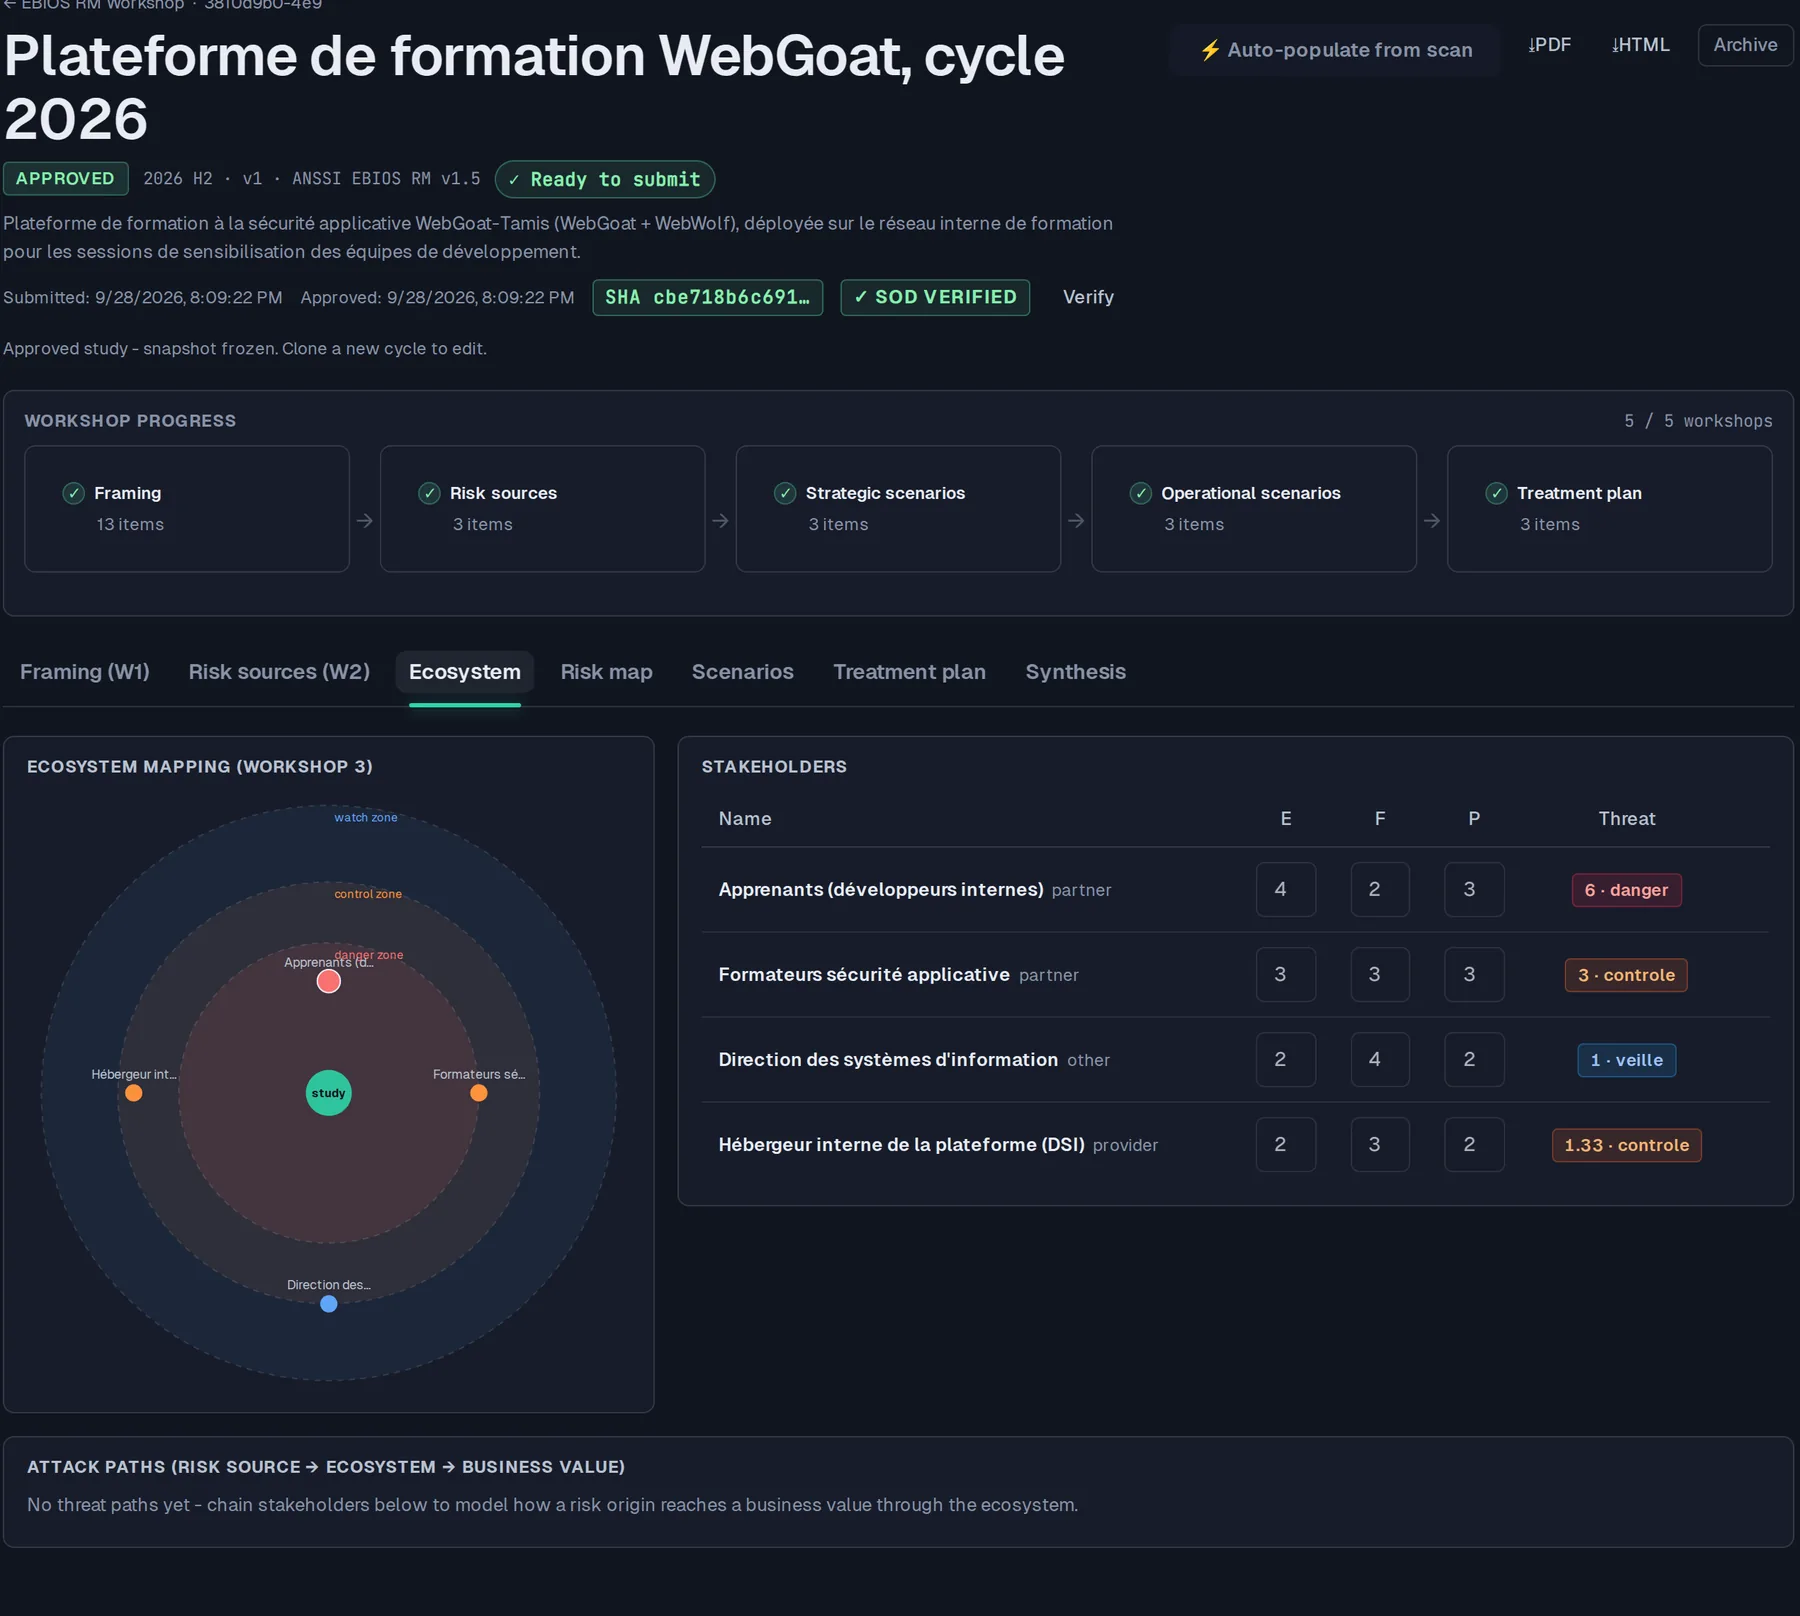
    Work through the five workshops with proposals drawn from your scans.
    Deployment
    SaaS in the EU (OVHcloud or Scaleway) or self-hosted, air-gapped included

    In Tamis

    Make decisions with evidence at hand.

    Prepare your decisions and board pack

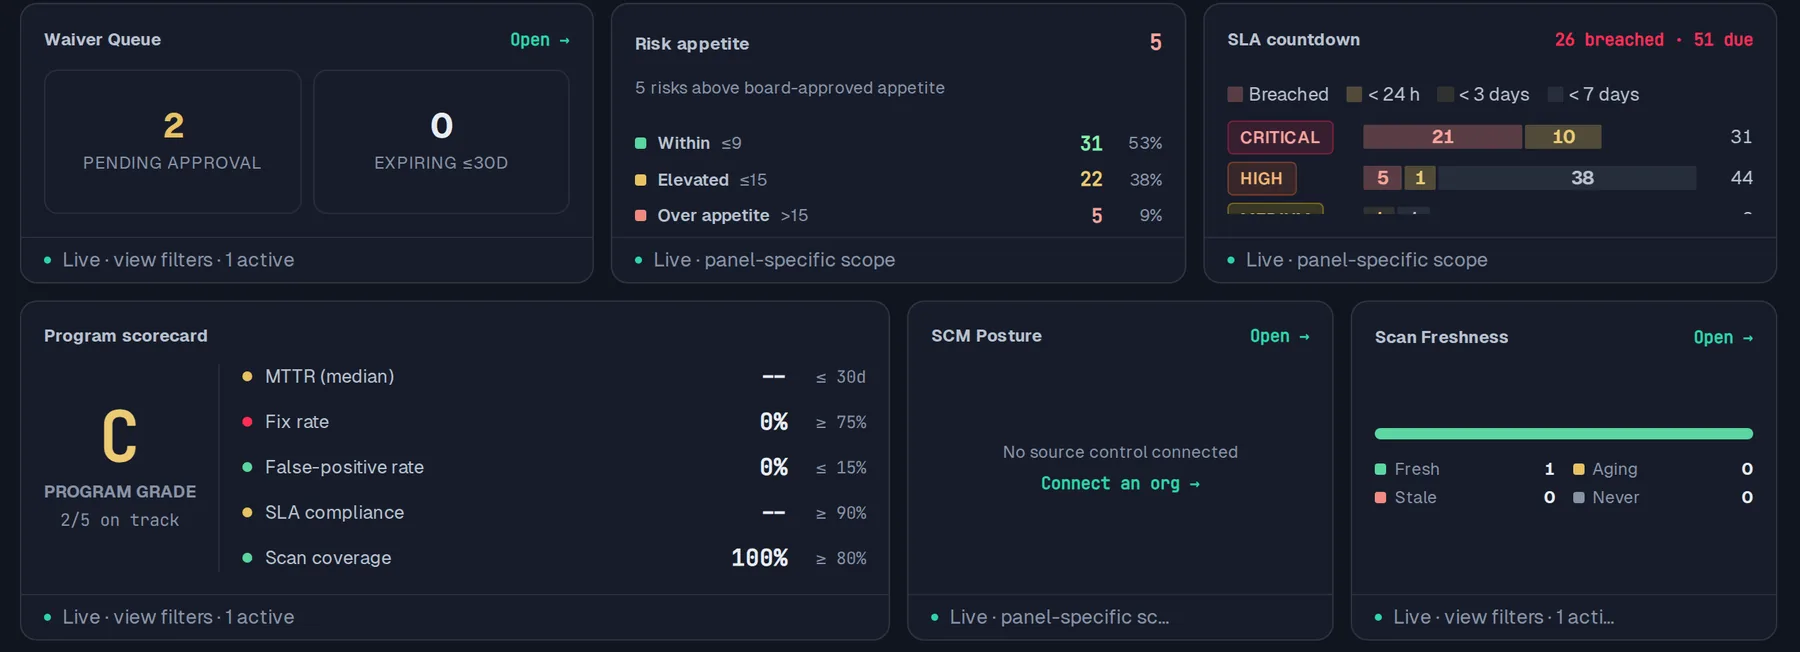
    The cockpit brings remediation, attack chains, chokepoints and closed controls together in at most twenty actions per project.

    Every action shown is backed by evidence.

    You can export the pack as PDF, DOCX or PPTX, with your branding and risk-appetite thresholds.

    Track your risks and their treatment

    You can give every risk a treatment, an owner and a due date.

    You can also link it to the finding or EBIOS scenario that justifies it.

    Depending on severity, acceptance requires one to three approvals.

    Approvers can be neither the requester nor the risk owner.

    Run your EBIOS RM workshops

    You work through all five workshops to the treatment decision.

    Attack chains associated with findings can inform operational scenarios, to be validated in the workshop.

    Accepting a risk requires approval from someone other than its author.

    Connect findings to frameworks

    You have 16 frameworks, including ISO 27001, NIS2, SecNumCloud, HDS and PGSSI-S.

    Their 224 controls are linked to the CWEs detected by your scans.

    In development: a NIS2 classification suggested from the information you provide.

    Track regulatory deadlines

    A KEV or EPSS signal can trigger an internal 24-hour follow-up for you to qualify.

    The incident register calculates NIS2 and DORA reporting deadlines to help you track them.

    Gather evidence for audit

    Your vendors respond through a token link that expires and can be revoked.

    You choose what your trust center publishes.

    Your auditors can draw an evidence sample with separation of duties.

    On the same evidence

    What moves between roles.

    You receive

    • STRIDE threats and EBIOS scenarios prepared by the architect.
    • Qualified findings and verified fixes, accompanied by their evidence.
    • Pentest retests and reports to inform your decisions.

    You pass on

    • Decisions supported by risk scores to guide the next design.
    • Evidence packs to review and present to auditors and the board.
    • Treatment priorities that lead to reopening a control or finding.

    Good to know Tamis helps you measure readiness.
    It issues no certification or attestation.
    Only an external decision recorded by an authorized person is authoritative.

    From a project risk to a traceable decision.

    In the demo, examine a risk's evidence, its treatment and the material prepared for review.

    See pricing 

    Request a demo 

    On the blog

    Go further.

    The mechanics explained simply, then in depth. All articles